The threat has changed
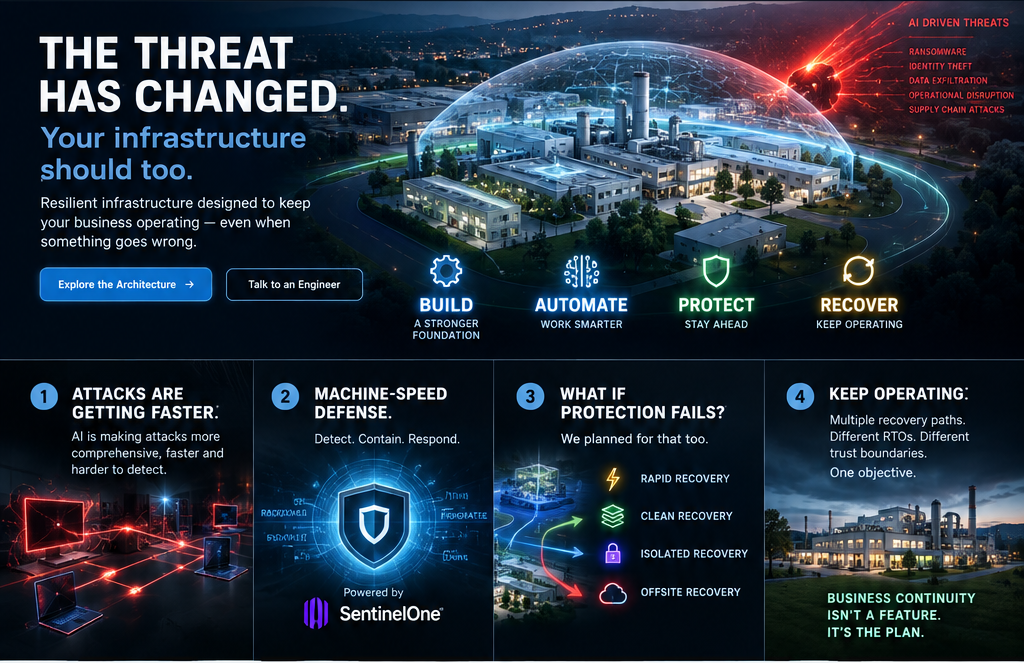
Why we are moving
to SentinelOne
The evolution of our endpoint protection strategy.
GDP has always believed in layered protection. That philosophy has not changed. The threat has changed. The speed of attack has changed. And the technology available to respond has changed.
“My thinking about cybersecurity has evolved as the threat has evolved.”
From removal to response.
We originally moved clients to Sophos because it connected the firewall and the endpoint. When malicious activity was detected, an endpoint could be isolated so the event could be investigated. That moved protection beyond traditional antivirus.
WE’RE NOT ABANDONING IT.
WE’RE TAKING THE NEXT STEP.
Known bad is no longer the whole story.
Signature detection asks whether a file is already known to be malicious. Modern attacks may instead use stolen passwords, scripts, PowerShell, legitimate utilities, or compromised trusted software.
Everything can look normal—except the trusted update became the attack.
WHAT IS THIS COMPUTER ACTUALLY DOING?Speed changes
everything.
We no longer believe we have the luxury of time. Automated digital attacks can operate faster than a human alert-and-investigation workflow.
OUR PROTECTION HAS TO OPERATE
AT THE SPEED OF THE DATA.
Technology brings
Speed
Scale
Continuous observation
Immediate action
People bring
Judgment
Experience
Business context
Decision-making
WE NEED MACHINES RESPONDING TO MACHINES
— WITH PEOPLE IN CONTROL.
Aggressive means earlier detection, faster investigation, and faster containment—not reckless behavior.
How SentinelOne works
- WATCH
Endpoint Agent
Provides activity visibility on the protected endpoint.
- DETECT
Behavioral AI
Looks at what software is doing—not only whether a file is already known to be bad.
KNOWN BAD FILE → BLOCK
ACTIVITY → BEHAVIOR → SUSPICIOUS PATTERN - UNDERSTAND
Storyline
Connects related activity: what started it, what happened next, which processes were involved, and what they touched.
- INVESTIGATE
Purple AI
Assists analysis and investigation. It supports people; it does not replace their judgment.
THE INVESTIGATION CAN BEGIN WHILE THE EVENT IS OCCURRING. - RESPOND
Hyperautomation
Runs predefined workflows according to established policies. Some actions can be automated; others can include human approval gates.
SOMETHING HAPPENED → SOMETHING IS BEING DONE ABOUT IT.
Capabilities depend on configuration and the selected protection level.
Stop the spread.
An endpoint may be the doorway rather than the final target.
ISOLATE THE PROBLEM,
NOT THE BUSINESS.
What about the damage already done?
Stopping an attack does not undo changes already made. Where supported and appropriate, rollback can help reverse malicious changes.
24×7 human security monitoring
AI and automation provide speed. Our strategy should not depend solely on automation—or on GDP seeing a 2:00 a.m. alert.
Vigilance services and response actions depend on the purchased service, configuration, and authorization.
SentinelOne understands the endpoint.
Vigilance understands the security incident.
GDP UNDERSTANDS
THE CLIENT.
We know the production servers, engineering workstations, proprietary systems, network, backup environment, recovery strategy, and the people responsible for the business.
The philosophy hasn’t changed.
The timeline has.
DETECT → ISOLATE → HUMAN INVESTIGATION → RESPOND
WATCH → DETECT BEHAVIOR → UNDERSTAND → AI-ASSISTED INVESTIGATION → AUTOMATED RESPONSE → CONTAIN / ISOLATE → ROLLBACK WHERE APPROPRIATE → 24×7 VIGILANCE → GDP REVIEW & COORDINATION
Reducing the timeline reduces the attacker’s operating time.
Not every computer has the same value or represents the same risk.
General office workstation
Engineering or proprietary system
Production system or critical server
WHAT LEVEL OF PROTECTION DOES THIS SYSTEM ACTUALLY REQUIRE?
Match protection and monitoring to ROLE · RISK · BUSINESS VALUE. Specific SentinelOne tiers will only be shown after GDP confirms licensing and deployment.
Better security doesn’t have to mean maximum cost on every endpoint.
Additional investment can be concentrated where exposure is greatest. Depending on current Sophos licensing, endpoint count, and selected SentinelOne protection levels, this can represent thousands per year in endpoint-security savings—but savings are not guaranteed.
PROTECT THE SYSTEM ACCORDING TO ITS VALUE TO THE BUSINESS.Put the security investment where the risk is.
SentinelOne is one layer.
Each layer has a different job. No layer is expected to be perfect.
We still plan for recovery.
We know firsthand that good backup and disaster recovery work—but they take time. Systems must be evaluated, data trusted, and services restored and tested. We would rather isolate a contained workstation than restore servers.
This isn't simply replacing one antivirus with another.
It is the continuation of a strategy we have developed for years. Sophos moved us beyond traditional antivirus by connecting endpoint protection with network containment.
The threat continued to evolve. So did my thinking.
SentinelOne advances that strategy with behavioral detection, AI-assisted investigation, automated response, containment, rollback where supported, and 24×7 managed monitoring where included—plus flexibility to better match protection and cost to each system.
OUR FIRST RESPONSE HAS TO AS WELL.FOR PROTECTION TO BE EFFECTIVE, IT MUST BE MORE AGGRESSIVE THAN THE ATTACK.
Protection must also be controlled, layered, and designed around the business.
THAT’S WHY WE’RE MOVING TO SENTINELONE.
Official SentinelOne references
For current product details, capabilities, and limitations, refer to SentinelOne’s official material. Availability depends on licensing and configuration.
- Endpoint SecurityOverview of endpoint protection, detection, response, and remediation.
- Singularity EndpointEndpoint product overview and current packaging information.
- Purple AIAI-assisted security analysis and investigation.
- Singularity HyperautomationPolicy-driven workflows with automated steps and human approval gates.
- Vigilance MDRManaged detection, investigation, and response services.
- Manufacturing SecuritySecurity considerations for manufacturing environments.
- Resource CenterCurrent datasheets, briefs, reports, and educational resources.